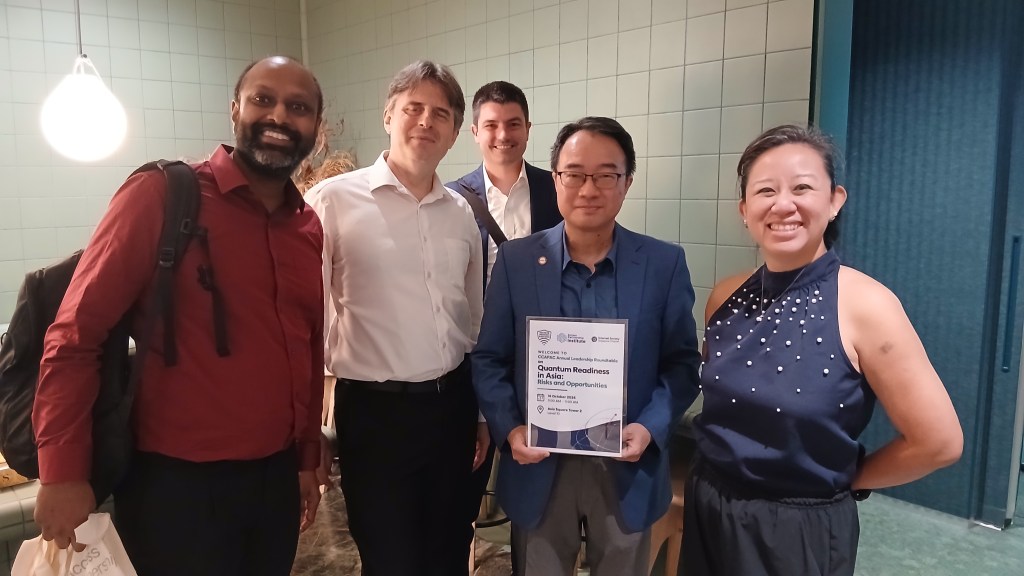
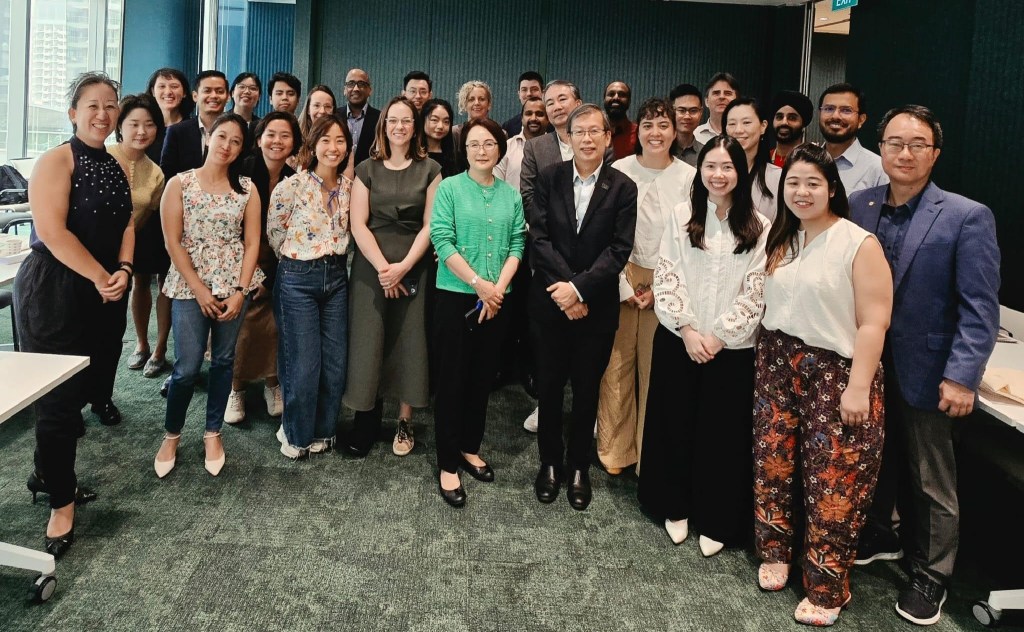
16 Oct 2026 : The Coalition for Cybersecurity in Asia Pacific (CCAPAC), the Access Partnership Institute, and Internet Society Singapore Chapter (ISOC SG) hosted CCAPAC’s annual Leadership Roundtable on Regional Cybersecurity Policy in Asia Pacific, as a fringe event around the Singapore International Cyber Week (SICW), to discuss the state of quantum computing and post-quantum cryptography (PQC) across Asia Pacific markets. The event launched CCAPAC’s Annual Report 2026 Quantum Readiness in Asia: Risks and Opportunities, covering Australia, China, India, Japan, Singapore, and South Korea.
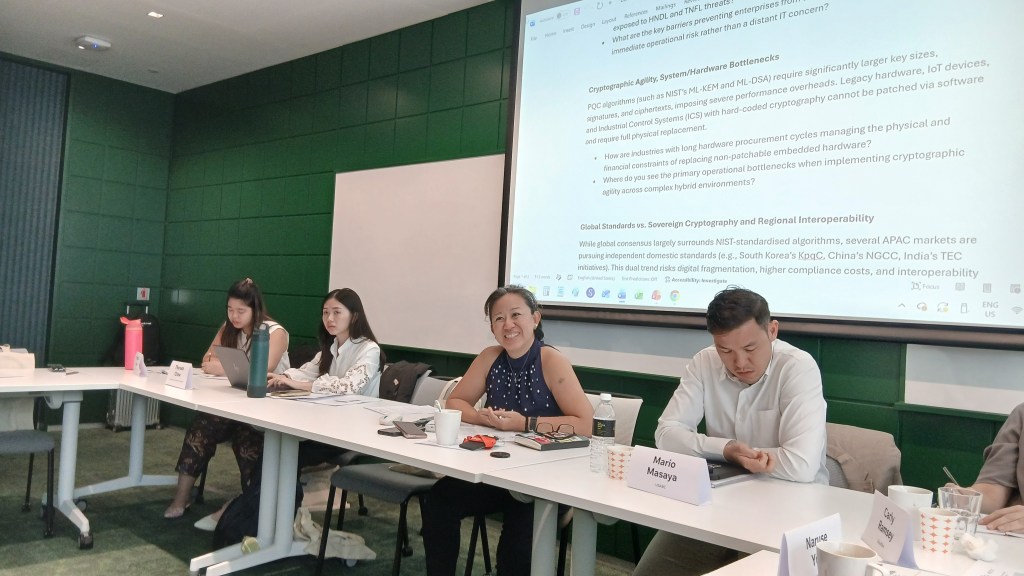
Readiness Findings
- The report assesses six impact markets and finds progress steady but uneven, and insufficient for emerging quantum security timelines. No market reviewed is fully prepared.
- Key gaps include incomplete cryptographic inventories, low awareness of harvest-now-decrypt-later and trust-now-forge-later risks, scarce PQC skills, limited SME awareness and fragmented standards.
- PQC runs on classical hardware; unlike PQC, quantum key distribution requires dedicated quantum communications infrastructure. Hybrid migration can help in the near term, but adds complexity, cost and attack surface.
Regional Approaches
- Australia has issued practical guidance and introduced government requirements for transition plans and PQC-ready procurement.
- Japan plans government migration by 2035, with earlier consideration for highly sensitive systems.
- India has published CII milestones through 2029 and enterprise milestones through 2033; officials have indicated the pace may need to increase.
- China has deployed QKD networks and services, while standards divergence may complicate interoperability.
- Singapore, South Korea and Taiwan also have national strategies, guidance, pilots or planned migration policies at different stages.
Discussion and Open Questions
- Participants stressed that procurement, inventories, standards alignment and critical-infrastructure planning are central.
- Treat quantum resilience as a national resilience issue
- Views differed on urgency and scope: which data needs protection over a decade or longer, and how should organisations prioritise when migration is difficult?
- Participants also raised authentication, hardware signatures, digital assets and the risk of divergent national standards.
- How can public communications make a technical, future-facing threat meaningful without overstating it?
- How can governments offer practical procurement examples and support organisations that cannot migrate every legacy system?
Report Scope and Findings
- The report reviews post-quantum cryptography readiness across six Asia-Pacific markets; its central finding is that readiness is uneven and inadequate for anticipated timelines.
- It distinguishes harvest-now-decrypt-later from trust-now-forge-later risks and explains that PQC can run on existing classical hardware, whereas QKD requires dedicated infrastructure.
Market Readiness
- Australia: government transition-plan and procurement requirements, practical guidance and variable sector readiness.
- China: significant quantum investment and QKD deployments; potential standards divergence and no national mandatory PQC deadline identified in the report.
- India: National Quantum Mission funding and published migration milestones, with discussion that timelines may accelerate.
- Japan: government migration target of 2035; sensitive systems may need earlier transition. Yuki described work on inventories, vendor dependencies and evaluation.
- Singapore, South Korea and Taiwan: strategies and initiatives at differing stages, including planned Taiwan government migration policy by the end of 2026.
Migration Priorities
- The report recommends executive-level risk consideration, cryptographic inventories, readiness planning, hybrid approaches and PQC-ready procurement.
- Government priorities include international standards alignment, critical-infrastructure planning, pilot programmes, SME incentives and workforce development.
- Participants highlighted procurement as a lever, alongside crypto agility, legacy equipment constraints and the need for practical guidance on systems that cannot yet migrate.
Open Discussion
- Participants debated how to communicate the threat and balance urgency with realistic risk prioritisation, including the long-term sensitivity of stored data.
- Topics included authentication and hardware signatures, digital assets, interoperability, standards trust and support for countries with limited capacity.